Developers can now build XRPL wallets into apps via Privy, with support for XRP, RLUSD, AI agent payments and x402.
 Live Chat
Developers can now build XRPL wallets into apps via Privy, with support for XRP, RLUSD, AI agent payments and x402.
Start every day with the top news stories right now, plus original features, a podcast, videos and more.
Hundreds of Ethereum wallets that had sat untouched for years were drained into the same tagged address, turning old key exposure into this week’s sharpest crypto security warning.
On Apr. 30, WazzCrypto flagged the incident affecting mainnet wallets on X, and their warning spread quickly because the affected accounts did not appear to be freshly baited hot wallets. They were old wallets with quiet histories, some tied to assets and tooling from an earlier Ethereum era.
Over 260 ETH, roughly $600,000, was drained from hundreds of dormant wallets. More than 500 wallets appear to be affected, with losses totaling roughly $800,000, and many wallets have been idle for four to eight years. The related Etherscan address is labeledFake_Phishing2831105, and shows 596 transactions, and records a 324.741 ETH movement to THORChain Router v4.1.1 around the Apr. 30 window.
The constant across them is more important for now: long-idle wallets have been moved to a common destination, while the compromise path remains unresolved.
That unresolved vector makes the drain the strongest warning this week, following a surge in DeFi hacks. Protocol exploits usually give investigators a contract, a function call, or a privileged transaction to inspect.
Here, the central question sits at the wallet layer. Did someone obtain old seed phrases, crack weakly generated keys, use leaked private-key material, abuse a tool that once handled keys, or exploit another path that has yet to surface?
Public discussion has produced theories including weak entropy in legacy wallet tools, compromised mnemonics, trading-bot key handling, and LastPass-era seed storage. One affected user personally raised the LastPass theory.
The practical advice for users is limited but urgent. Idleness does not mitigate private-key risk. A wallet with value depends on the full history of the key, the seed phrase, the device that generated it, the software that touched it, and every place that secret may have been stored.
For users, the response is probably to inventory high-value old wallets, move funds only after setting up fresh key material through trusted hardware or modern wallet software, and avoid entering old seeds into checkers, scripts, or unfamiliar recovery tools. Revoking approvals helps for protocol exposure, including Wasabi’s user warning, but a direct wallet drain points first to key security rather than token approvals.
The wallet cluster landed amid April’s crypto exploit tally, which was already elevated. DefiLlama-linked reporting put April at roughly 28 to 30 incidents and more than $625 million in stolen funds. As of May 1, the live DefiLlama API showed 28 April incidents totaling $635,241,950.
A May 1 market thread captured the pressure point: this week’s wallet drains, Wasabi Protocol’s admin-key exploit, and April’s larger DeFi losses all hit control surfaces that ordinary users rarely inspect. The link across the month is architectural rather than attributional.
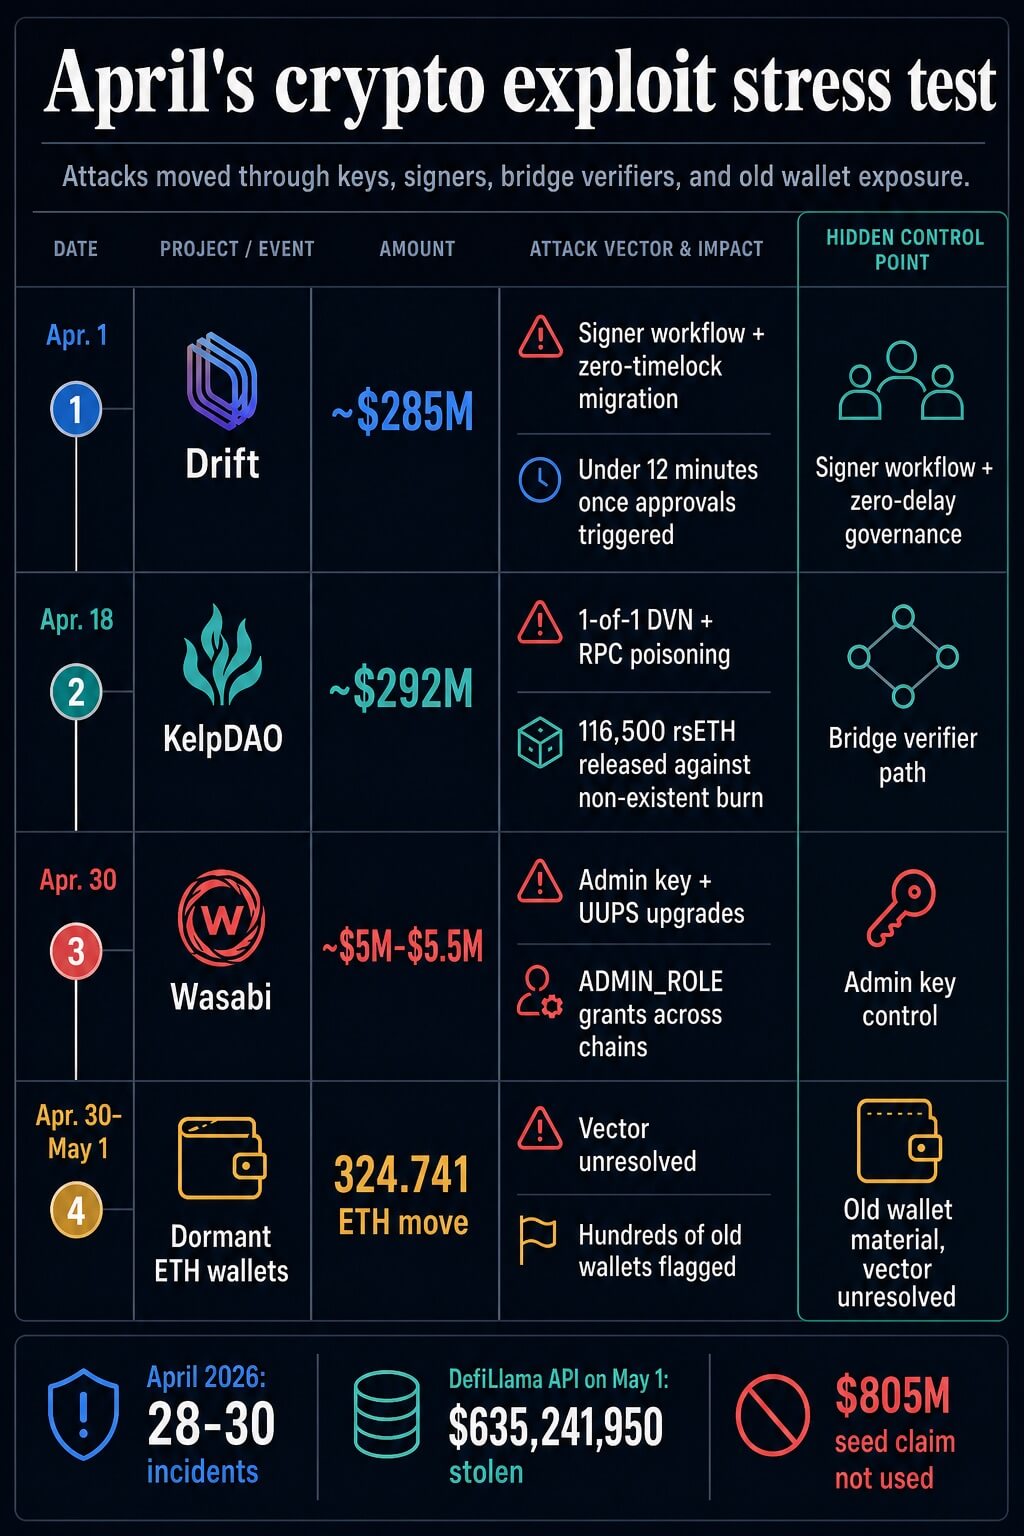
Wasabi Protocol supplies the clearest recent protocol example. The Apr. 30 exploit reportedly drained roughly $4.5 million to $5.5 million after an attacker gained deployer/admin authority, granted ADMIN_ROLE to attacker-controlled contracts, and used UUPS proxy upgrades to drain vaults and pools across Ethereum, Base, and Blast. Early security alerts flagged the admin-upgrade pattern as the attack unfolded.
The reported mechanics put key management at the center of the incident. Upgradeability can be normal maintenance infrastructure. Concentrated upgrade authority turns that maintenance path into a high-value target. If one deployer or privileged account can change implementation logic across chains, the boundary around an audited contract can vanish once that authority is compromised.
That is the user-facing problem hidden inside many DeFi interfaces. A protocol can present open contracts, public front ends, and decentralization language while critical upgrade power still sits in a small set of operational keys.
Drift pushed the same control problem into signer workflow. Chainalysis described social engineering, durable nonce transactions, fake collateral, oracle manipulation, and a zero-timelock 2-of-5 Security Council migration. Blockaid put the loss around $285 million and argued that transaction simulation and stricter co-signer policies could have changed the outcome.
The Drift case matters here because the path did not depend on a simple public-function bug. It depended on a workflow where valid signatures and fast governance machinery could be turned toward a hostile migration. A signer process became the control surface.
KelpDAO moved the stress test into cross-chain verification. The incident statement described a bridge configuration in which the rsETH route used LayerZero Labs as the sole DVN verifier. Forensic reviews described compromised RPC nodes and DDoS pressure feeding false data to a single-point verification path.
The result, according to Chainalysis, was 116,500 rsETH, worth roughly $292 million, released against a non-existent burn. The token contract could remain intact while the bridge accepted a false premise. That is why a verifier failure can become a market-structure problem once the bridged asset sits inside lending markets and liquidity pools.
I think Project Glasswing deserves a special mention here for context, separate from causation. Anthropic says Claude Mythos Preview found thousands of high-severity software vulnerabilities and shows how AI can compress vulnerability discovery. That raises the bar for defenders, but the causal record in these crypto incidents points to keys, signers, admin powers, bridge verification, RPC dependencies, and unresolved wallet exposure.
The security implications are still serious. Faster discovery gives attackers and defenders more parallel surface to work through. It also makes old operational shortcuts more expensive because dormant secrets, privileged keys, and single-verifier paths can be tested faster than teams can manually review them.
The controls that follow from April sit above and around the codebase.
| Incident | Hidden control point | Failure mode | Practical control |
|---|---|---|---|
| Dormant Ethereum wallets | Old wallet material | Funds moved from long-idle wallets into a tagged address while the vector remains unresolved | Fresh key generation for valuable dormant funds, cautious migration, and no seed entry into unknown tools |
| Wasabi | Admin and upgrade authority | Privileged role grants and UUPS upgrades enabled vault and pool drains | Key rotation, stronger thresholds, bounded admin powers, timelocks, and independent monitoring of upgrade actions |
| Drift | Security Council signer workflow | Pre-signed durable nonce transactions and zero-delay governance enabled fast admin takeover | Higher thresholds, delay windows, transaction simulation, and policy-enforced co-signing |
| KelpDAO | Bridge verification path | RPC poisoning and a 1-of-1 DVN route allowed a false cross-chain message to pass | Multi-DVN verification, cross-chain invariant monitoring, and independent checks outside the same verifier path |
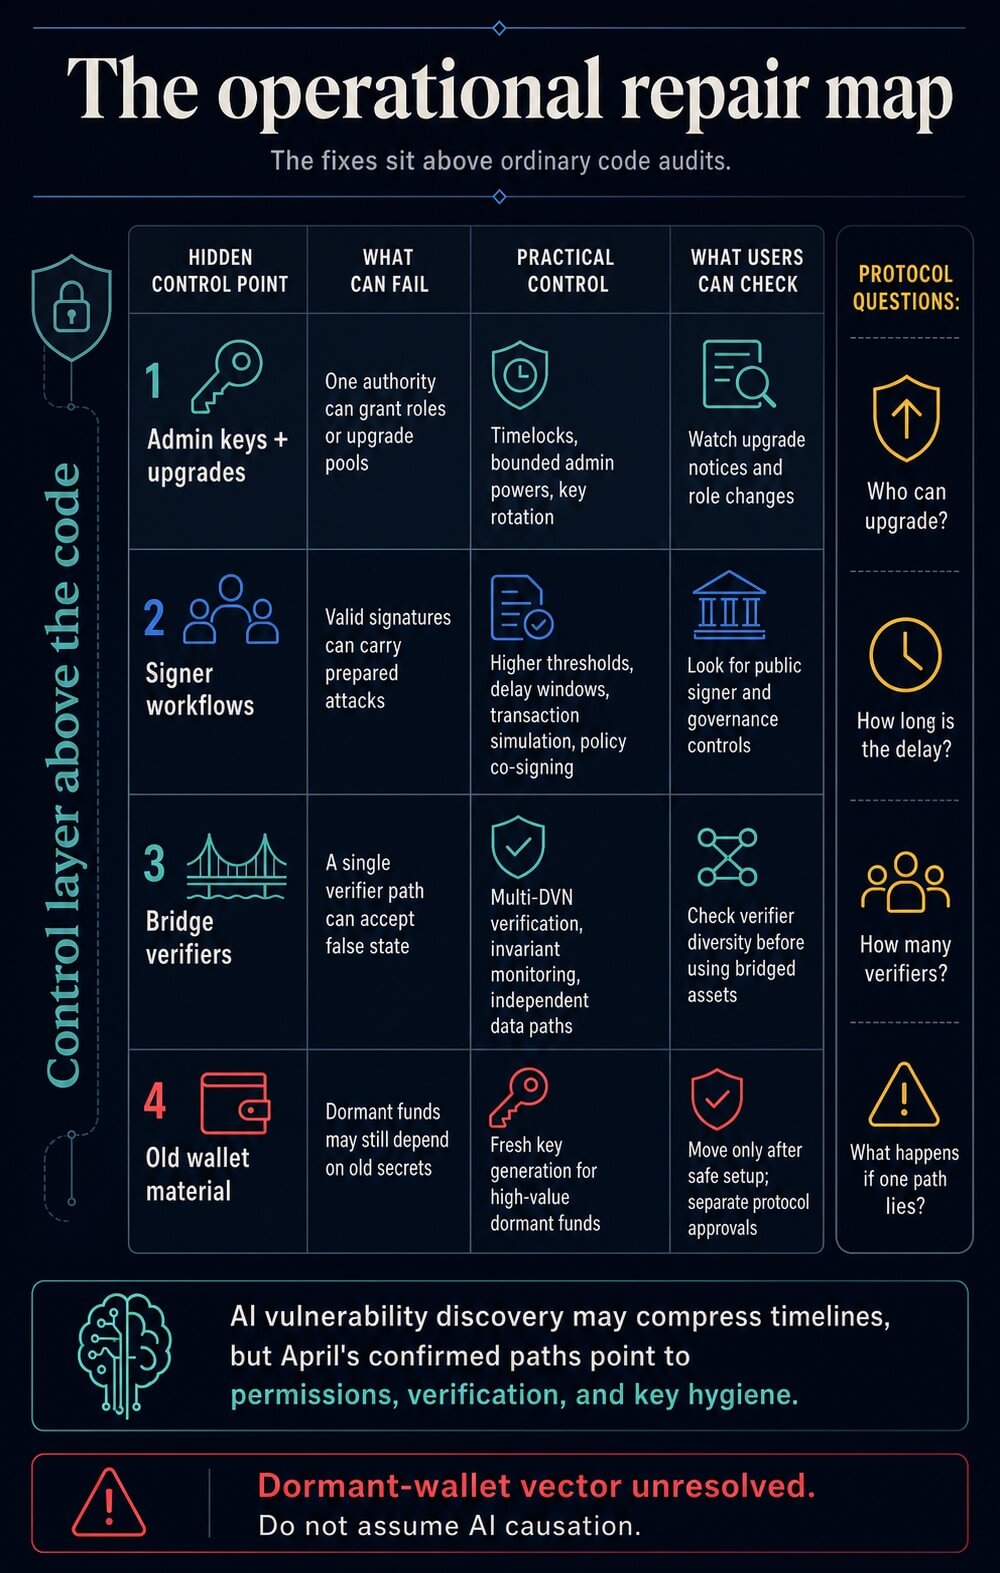
For protocols, the priority is to reduce the amount that any single authority can do at once. That means time locks on admin operations, stronger and more stable signer thresholds, monitored privileged-transaction queues, explicit limits on parameter changes, and co-signing systems that simulate transaction effects before humans approve them.
For bridges, the priority is independent verification and invariant checks. A cross-chain message should be tested against the economic fact it claims to represent. If rsETH leaves one side, the system should verify the corresponding state change on the other side before the destination side releases value. That monitoring needs to exist outside the same path that signs the message.
For users, the repair list is smaller. Move valuable old funds to fresh keys through a process you already trust. Separate that action from protocol-specific approval cleanup. Treat every claim about the wallet-drain root cause as provisional until forensic work identifies a common tool, storage path, or exposure source.
April proved that the average user’s security checklist is likely incomplete. Audits, public contracts, and decentralized interfaces can coexist with concentrated admin authority, weak signer procedures, brittle bridge verification, and old wallet secrets.
The next quarter will reward proof over decentralization language: constrained upgrade powers, visible timelocks, independent verifier paths, transaction simulation for privileged actions, disciplined access controls, and documented key rotation.
The dormant-wallet drains show the uncomfortable user-side version of the same problem. A system can look quiet while an old control failure waits in the background. April’s exploit wave exposed that layer above the code; the next phase will show which teams treat it as core security before funds move.
Two Bitcoin wallets linked by analysts to Silk Road–era activity last moved 3,421 BTC in May this year. Now, follow-on activity on Dec. 10 added a fresh pulse to a year of dormant-supply awakenings.
According to the Digital Watch Observatory, the May spends totaled about 3,421 BTC, roughly $322.5 million at the time.
The sequence included a 2,343 BTC outlay at block height 895,421 that rerouted outputs into a new SegWit address pattern.
On-chain forensics show 31 outputs with consolidation into a new P2WPKH destination, a pattern more consistent with custody housekeeping than immediate exchange deposition.
Trackers on Dec. 10 flagged additional consolidation totaling just over $3 million from over 300 wallets labeled as Silk Road–linked, maintaining attention on these addresses and inviting a near-term read on whether labels or routing matter more for price discovery.
The December flows were small in BTC terms relative to the May sequence, although still timely given renewed sensitivity to old-coin movements this year.
That sensitivity has been shaped by episodes in which government-controlled Silk Road coins were routed to Coinbase Prime, a step traders treat as a sale-preparatory move.
The U.S. government transferred 10,000 BTC to Coinbase Prime in August 2024 and about 19,800 BTC in December 2024, and these transfers have coincided with short-lived risk-off positioning in the days around the transfers.
The May wallets were initially created in July 2013 and then were silent for about 11 to 12 years before spending, which anchors the setup for a dormant-supply narrative.
The output structure during the May sequence leaned toward consolidation and re-keying, with fresh Bech32 custody destinations rather than exchange-labeled deposit heuristics.
That distinction shapes trader response, because flows into Coinbase Prime or other prime broker venues are treated as near-term supply, while internal consolidation to P2WPKH does not imply imminent distribution.
A practical way to compare scale and routing is to line up the Silk Road–linked wallet moves against two prior U.S. government transfers that hit Coinbase Prime.
The amounts involved in 2024 were an order of magnitude larger than the May 2025 dormant-wallet spends, which helps explain why market participants prioritize exchange-tagged receipts over unlabeled consolidations.
| Date window | Controller / label | Amount (BTC) | Approx. USD at time | Routing pattern |
|---|---|---|---|---|
| May 5–7, 2025 | Silk Road–linked wallets | 3,421 | ~$322.5M | Consolidation to new P2WPKH |
| Aug. 2024 | U.S. government, Silk Road seizures | 10,000 | ~$600M | To Coinbase Prime |
| Dec. 2024 | U.S. government, Silk Road seizures | ~19,800 | ~$2B | To Coinbase Prime |
| Dec. 10, 2025 | Silk Road–linked wallets | ~$3M equivalent | — | Follow-on consolidation |
The category of Silk Road coins has a long public track record through auctions, seizures, and more recent exchange-routed transfers. In 2014, the U.S. Marshals Service auctioned 29,656 BTC seized from Silk Road, a sale won by Tim Draper, which set an early playbook for transparent liquidation.
That auction demonstrated that official supply could be scheduled and absorbed without an opaque drip. The approach has evolved. The Department of Justice and IRS-CI later seized 69,370 BTC tied to “Individual X” in 2020 and 50,676 BTC from James Zhong, announced in 2022, with sentencing in 2023.
A 2023 court filing outlined a staged liquidation of about 41,490 BTC from the Zhong cache during 2023, which gave markets interim visibility into execution but still left timing risk around transfer days.
Coinbase Prime receipts, or other exchange-labeled custody endpoints, are read as a prelude to distribution through OTC or block trading, which can compress basis and nudge funding toward neutral as desks hedge inventory.
Consolidation to fresh P2WPKH addresses, by contrast, aligns with internal re-keying or moving to updated custody stacks, which carries a lower immediate sale probability.
The May 2025 paths fit the latter mold, while the larger 2024 government transfers fit the former, which has been the trigger for option skew to lean put-heavy and for implied volatility to pop in short tenors.
Market structure in December 2025 adds another layer. Record outflows from U.S. spot Bitcoin ETFs in November, followed by renewed inflows in early December, left traders focused on the balance between passive demand and any labeled supply.
Weekly fund-flow swings remain the highest-frequency barometer for direction, and flows can offset or amplify the signal from labeled on-chain transfers. If exchange tags do not appear after a labeled wallet spends, realized volatility tends to mean-revert as liquidity providers normalize their inventory.
A benign consolidation path, with a 40–55% probability, would involve continued migration to fresh SegWit or Bech32 custody without exchange tags. The outcome would be a short headline window, fading option skew, and a return to ETF-led tape.
A stealth OTC distribution path, with a 25–35% probability, would see coins route to a prime broker like Coinbase Prime and then move through block trades, producing mild and persistent ask-side pressure and compressing basis while funding moderates.
A headline-driven de-risk path at 10–20% would require new, larger government transfers in the 10,000-20,000 BTC range that coincide with a weak ETF flow day, triggering rapid downticks as miners and perpetual traders sell into the move. The 2024 transfer playbook is the best analog for that third scenario.
There have been multiple Satoshi-era awakenings this year, and a wave of cohort spends older than 7 years into the fourth quarter, which helps explain why even modest December movements from Silk Road–linked labels still register in positioning.
That said, on-chain details remain the first filter. P2WPKH consolidation, fresh custody destinations, and the absence of exchange-labeled receipts within 24 to 72 hours have aligned with low follow-through on price in prior cases.
Conversely, Arkham or Whale Alert flags that explicitly show Coinbase Prime receipts, paired with mid-day U.S. prints, have coincided with short-term inventory hedging, wider short-dated put skew, and a softer basis.
History provides grounding. The first major public liquidation in 2014 through the USMS auction showed that scheduled, transparent sales can be absorbed. Subsequent seizures, including the 69,370 BTC linked to “Individual X” and the 50,676 BTC from James Zhong as noted by the Department of Justice, moved into a framework where courts cleared liquidation pathways.
A 2025 court decision declined to block the sale of a separate 69,370 BTC cache, effectively keeping the legal channel open.
For the immediate tape, the watchlist is straightforward. Look for exchange-labeled receipts, especially Coinbase Prime, in the days after any fresh Silk Road–linked spend.
Track daily ETF flow direction, since the interaction between passive demand and labeled supply governs whether headlines fade or drive a broader de-risk. Monitor the options surface for short-dated skew leaning toward puts, along with quick changes in perpetual funding and futures basis on transfer days, which serve as positioning tells.
However, given that billions of dollars’ worth of Bitcoin is now regularly absorbed by ETF liquidity each week, it is unlikely that any Silk Road sales would materially affect the Bitcoin price without some other psychological catalyst.
According to the Digital Watch Observatory, the May 2025 pattern points to consolidation over distribution, and the Dec. 10 activity remains consistent with that base case until exchange tags appear.